Hello! Welcome to the final lesson of the "Privilege Escalation & Post-Exploitation" module.
In our previous lesson, you mastered the art of establishing persistence, ensuring your access to a compromised system survives reboots and other disruptions. However, the very actions of gaining access, escalating privileges, and setting up backdoors have left a trail of evidence—command histories, log entries, and uploaded files. A skilled defender or forensic investigator can follow this trail directly back to you.
This lesson is about erasing that trail. We will delve into the world of anti-forensics, focusing on the practical techniques used to cover your tracks. By the end of this lesson, you will know how to effectively clean up artifacts and payloads from a compromised system to minimize the chances of detection.
1. The Art of Invisibility: Principles of Covering Tracks
The goal of covering your tracks is to make a forensic investigation as difficult as possible. This goes beyond simply deleting files. A missing log file is often as loud, if not louder, than a log file containing malicious activity. True stealth lies in subtlety.
The core principles are:
- Remove Payloads: Delete any tools, scripts, or executables you've uploaded to the target.
- Erase History: Clear command-line history that documents your actions.
- Sanitize Logs: Remove or alter log entries that record your intrusion, access, and activities.
- Alter Timestamps: Modify the timestamps of files you've touched to blend them in with legitimate system files.
Let's begin with the fundamental techniques for log and history manipulation on Linux systems.
How Hackers Clear Tracks after Hacking | Clear Logs & History
The video 'How Hackers Clear Tracks after Hacking' by HackHunt provides a practical overview of basic cleanup tasks on a Linux machine. It clearly demonstrates the difference between deleting a log and emptying it.
Watch the video from 00:38 to 03:17. Pay close attention to these three key actions: Clearing the command history (history -c). Removing critical log files like auth.log and syslog. Using the truncate command as a stealthier alternative to rm for emptying logs.
As the video shows, using truncate -s 0 <logfile> makes the file empty but leaves the file itself intact. This is less likely to trigger a simple alert that checks for the existence of a log file, making it a preferable technique over rm.
2. Linux Cleanup in Practice
Let's organize our Linux cleanup process methodically.
Command History
The bash shell, by default, records every command you type into a file, typically ~/.bash_history.
- Temporary Purge:
history -cclears the history for the current session. - Permanent Purge:
rm ~/.bash_historyremoves the file entirely. - Proactive Evasion: For future operations, you can prevent history from being saved in the first place by setting environment variables:
unset HISTFILEorexport HISTSIZE=0.
System Logs
The /var/log directory is the central repository for logs on Linux. Key files to be aware of include:
/var/log/auth.log(or/var/log/secureon Red Hat-based systems): Authentication events, including SSH logins andsudousage./var/log/syslog(or/var/log/messages): General system messages./var/log/wtmp: Records of all user logins and logouts./var/log/btmp: Records of failed login attempts.
While you can truncate these files, be aware that on a system with a mature security posture, these logs are likely being forwarded in real-time to a central log server or SIEM (Security Information and Event Management) system. In such cases, cleaning local logs is of limited value.
Payloads and Tools
You must remove any tools you've uploaded. A simple rm is often insufficient, as the data can potentially be recovered from the disk.
How Hackers Clear Tracks after Hacking | Clear Logs & History
Let's return to the HackHunt video to see how to securely delete files and remove any installed packages.
Watch from 04:02 to 05:34. This section introduces the shred command for secure file deletion and apt remove --purge for uninstalling tools.
The shred command overwrites a file multiple times, making it practically impossible to recover. This is a critical tool for destroying sensitive data and your offensive toolkit.
File Timestamps (Timestomping)
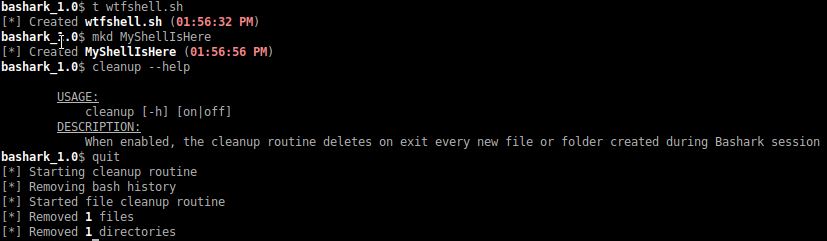
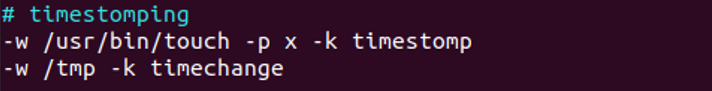
After placing a backdoor or tool on a system, its timestamp (creation/modification date) will stick out. Timestomping is the act of altering a file's timestamps to match those of legitimate system files, helping it blend in.
The touch command on Linux is perfect for this. The -r flag lets you use a reference file.
touch -r /bin/bash your_malicious_payload.sh
This command sets the timestamp of your_malicious_payload.sh to be identical to the timestamp of the /bin/bash executable, a common system file.
3. Windows Cleanup: A Higher Stakes Game
Cleaning up on Windows is more complex due to the centralized and structured nature of the Windows Event Log.
Cleaning Up Persistence
First, you must remove the persistence mechanisms you established in the previous lesson. The GitHub repository we reviewed has a section dedicated to this.
Advanced Windows persistence techniques and backdoor ...
Let's review the commands needed to reverse the persistence techniques we learned about. This is the first and most crucial step in your cleanup process.
Read the 'Cleanup Procedures' section. Note the commands used: reg delete, sc delete, schtasks delete, and del. These directly correspond to the creation commands we studied previously.
Windows Event Log Evasion
Simply deleting an event log file (.evtx) is not feasible on a running system. The standard approach is to use the built-in wevtutil.exe utility.
However, this is where the cat-and-mouse game truly begins. To understand the different levels of sophistication, we will watch a presentation from the SANS Institute, a leader in cybersecurity training.
What Event Logs? Part 1: Attacker Tricks to Remove Event Logs
The video 'What Event Logs? Attacker Tricks' provides an expert breakdown of how attackers defeat Windows Event Logging, from basic to highly advanced methods. This is essential knowledge for any professional.
This is a dense but critical video. Please watch the following segments carefully: The Basic Method (12:43 - 17:35): Learn how wevtutil cl is used to clear a log and why the resulting Event ID 1102 (The audit log was cleared) is a dead giveaway. The Advanced Method: Mimikatz (29:49 - 33:51): This is a game-changer. Understand how mimikatz's event::drop command patches the event logging service in memory to stop it from writing any new events, completely bypassing the Event ID 1102 artifact. The Expert Method: Thread Disruption (33:51 - 36:43): See how the Invoke-Phantom script takes this a step further by finding and killing the specific threads responsible for writing logs, making the service appear to be running normally. Detecting the Undetectable (36:43 - 42:15): Finally, understand the defender's perspective. Learn how even these advanced techniques can be detected by looking for surrounding artifacts (like evidence of tool execution), performing memory forensics, and correlating data from other log sources.
The key takeaway from the SANS video is that as an attacker, your techniques must evolve. A beginner clears logs and raises an alarm. An expert manipulates the logging process itself to create a "black hole" in the evidence trail. But even an expert can be caught by a defender who knows where else to look.
Proactive Anti-Forensics
Beyond active cleanup, advanced attackers configure the system to generate fewer artifacts in the first place.
The 'Anti-Forensic Study' by the NATO CCDCOE discusses several techniques, including how to configure Windows to minimize the digital footprints it creates.
Briefly skim Section 3.7 'Microsoft anti-forensic settings' (pages 59-61). You don't need to memorize the registry keys, but understand the types of artifacts that can be disabled, such as UserAssist logging, prefetching, and last access time updates.
4. Putting It All Together
Covering your tracks is an operational security (OpSec) discipline. It requires you to think like a defender and anticipate their investigation methods.
Test your understanding!
You have compromised a Windows Domain Controller and a Linux web server for a client with a very mature Security Operations Center (SOC). You know they forward all system and event logs to a central SIEM in real-time.
Which of your track-covering techniques would be least effective in this scenario? Which might still provide some value?
Show answer
-
Least Effective: Any action that involves clearing or modifying logs on the local host (e.g.,
wevtutil cl,truncate /var/log/auth.log, or evenmimikatz event::drop). Since the logs are shipped to the SIEM in real-time, the SOC already has copies. Tampering with the local logs after the fact is futile and will only create more noise, signaling that a cleanup attempt has occurred. -
Still Valuable:
- Securely Deleting Tools: Using
shredto remove your toolkit from the disk. This prevents a forensic analyst from recovering your specific payloads from a disk image. - Timestomping: Altering the timestamps of any remaining files (e.g., a persistence payload) to make them harder to spot in a file system timeline analysis.
- Clearing Command History: Removing
.bash_historyis still useful, as command history is typically not forwarded to a SIEM.
- Securely Deleting Tools: Using
These actions target artifacts on the host's disk and in its immediate memory, which may not be captured by remote logging, thus still providing value in hindering a deep-dive forensic investigation.
Conclusion
You have now reached the end of the post-exploitation phase. Covering your tracks is the final, crucial step that separates a clumsy intrusion from a professional, stealthy operation.
Key Takeaways:
- Track covering is essential for evading detection, maintaining long-term access, and frustrating forensic investigations.
- Simply deleting artifacts is noisy. Stealthier methods involve truncating files, modifying timestamps, and using advanced in-memory techniques.
- On Linux, focus on sanitizing command history (
~/.bash_history), system logs (/var/log), and usingshredandtouchto manage payloads and their timestamps. - On Windows, event log evasion is key. While basic cleanup uses
wevtutil, advanced attackers use tools like Mimikatz (event::drop) or PowerShell scripts to patch the logging service in memory, preventing detection of the cleanup itself. - Always operate with the assumption that logs are being centrally collected. Your goal is to make the investigator's job as difficult as possible, not to achieve perfect invisibility.
Next Lesson Preview:
With this module complete, you have now followed the full attack chain on a single machine: reconnaissance, exploitation, privilege escalation, persistence, and cleanup. In our next module, "Pivoting, Reporting, & Professional Practice," we will broaden our scope. You will learn how to use a compromised host as a pivot point to attack other machines on the internal network. We will also cover the critical skills of navigating bug bounty programs and writing professional, actionable vulnerability reports—the skills that turn hacking into a career.